+44 (0)1482 770583
 hello@systechitsolutions.co.uk
Cyber Essentials Made Simple: Prepared, Evidenced, Ready to Submit
A customer has asked for Cyber Essentials, with a date attached. We help you get there.
In this video
- Every question worked through with you, in plain English, across all five controls
- Gaps found and fixed first: MFA on cloud services, critical updates within 14 days, admin accounts, unsupported software
- Evidence gathered so every answer is true and ready to show
- You submit and sign; an independent Certification Body checks it and awards your certificate
- Kept ready for renewal, and for Cyber Essentials Plus if you need it
- Systech holds Cyber Essentials itself and is ISO 27001 certified
Talk it through with us
A short call about how things work for you today. We will tell you plainly where we would start, and if we are not the right fit.
Book a callTranscript
A customer's asked for Cyber Essentials, with a date attached. Then you open the questions.
Since April, a single missed setting, like MFA on a cloud service, can fail the whole assessment.
And it's worth it. The UK government says certified organisations are 92% less likely to make an insurance claim.
Systech gets you ready.
We work through every question with you, in plain English, across all five controls.
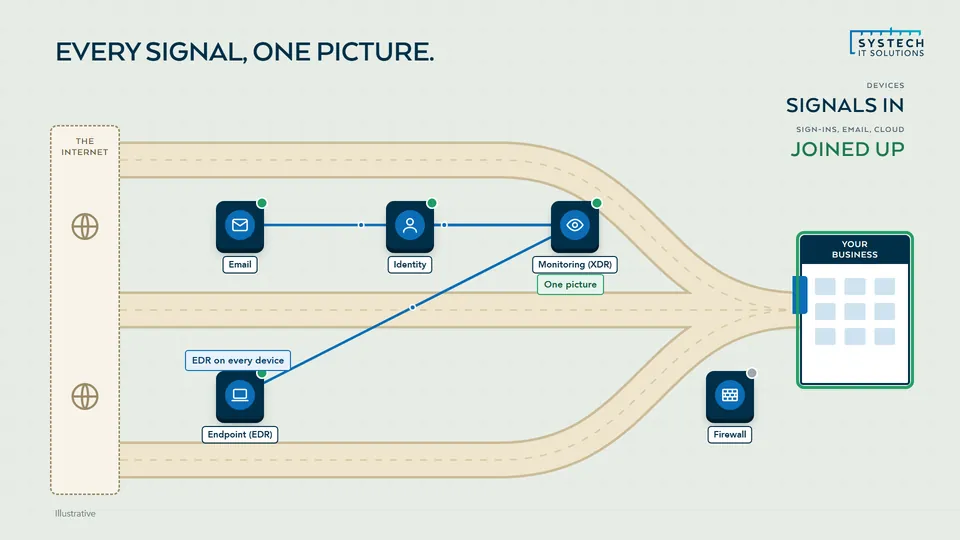
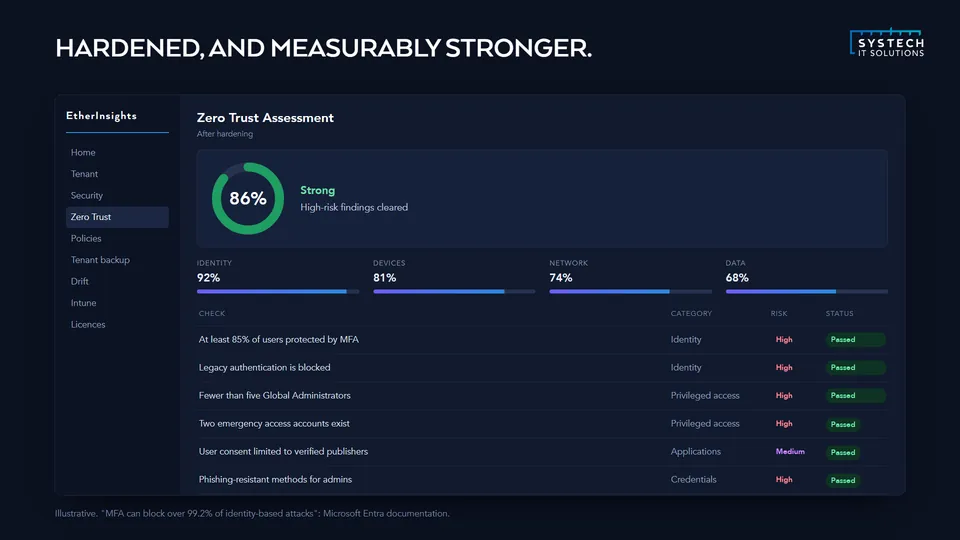
We find and fix the gaps first: MFA, patching within 14 days, admin accounts and unsupported software.
And we gather the evidence, so every answer is true and ready to show.
You submit and sign, then an independent assessor checks it and awards your certificate.
Then we keep you ready for next year's renewal, and for Cyber Essentials Plus if you need it.
We hold Cyber Essentials ourselves, and we're ISO 27001 certified.
Book a call, tell us your deadline, and we'll show you how we'd get you there.
Sources: NCSC Cyber Essentials Requirements for IT Infrastructure v3.3; UK government, Cyber Essentials 10 years on (2024). Systech is not a Certification Body; certificates are issued by IASME-licensed Certification Bodies.